Resources
Insights from Pistachio
Research, guidance and news on phishing, security awareness and insider threats.
About

This is where Pistachio shares what we learn from running phishing simulations, training and insider threat detection across hundreds of organisations. Expect research, practical guidance for IT teams and MSPs, and news from the team.
New articles, reports and product updates published regularly.
Featured Insight
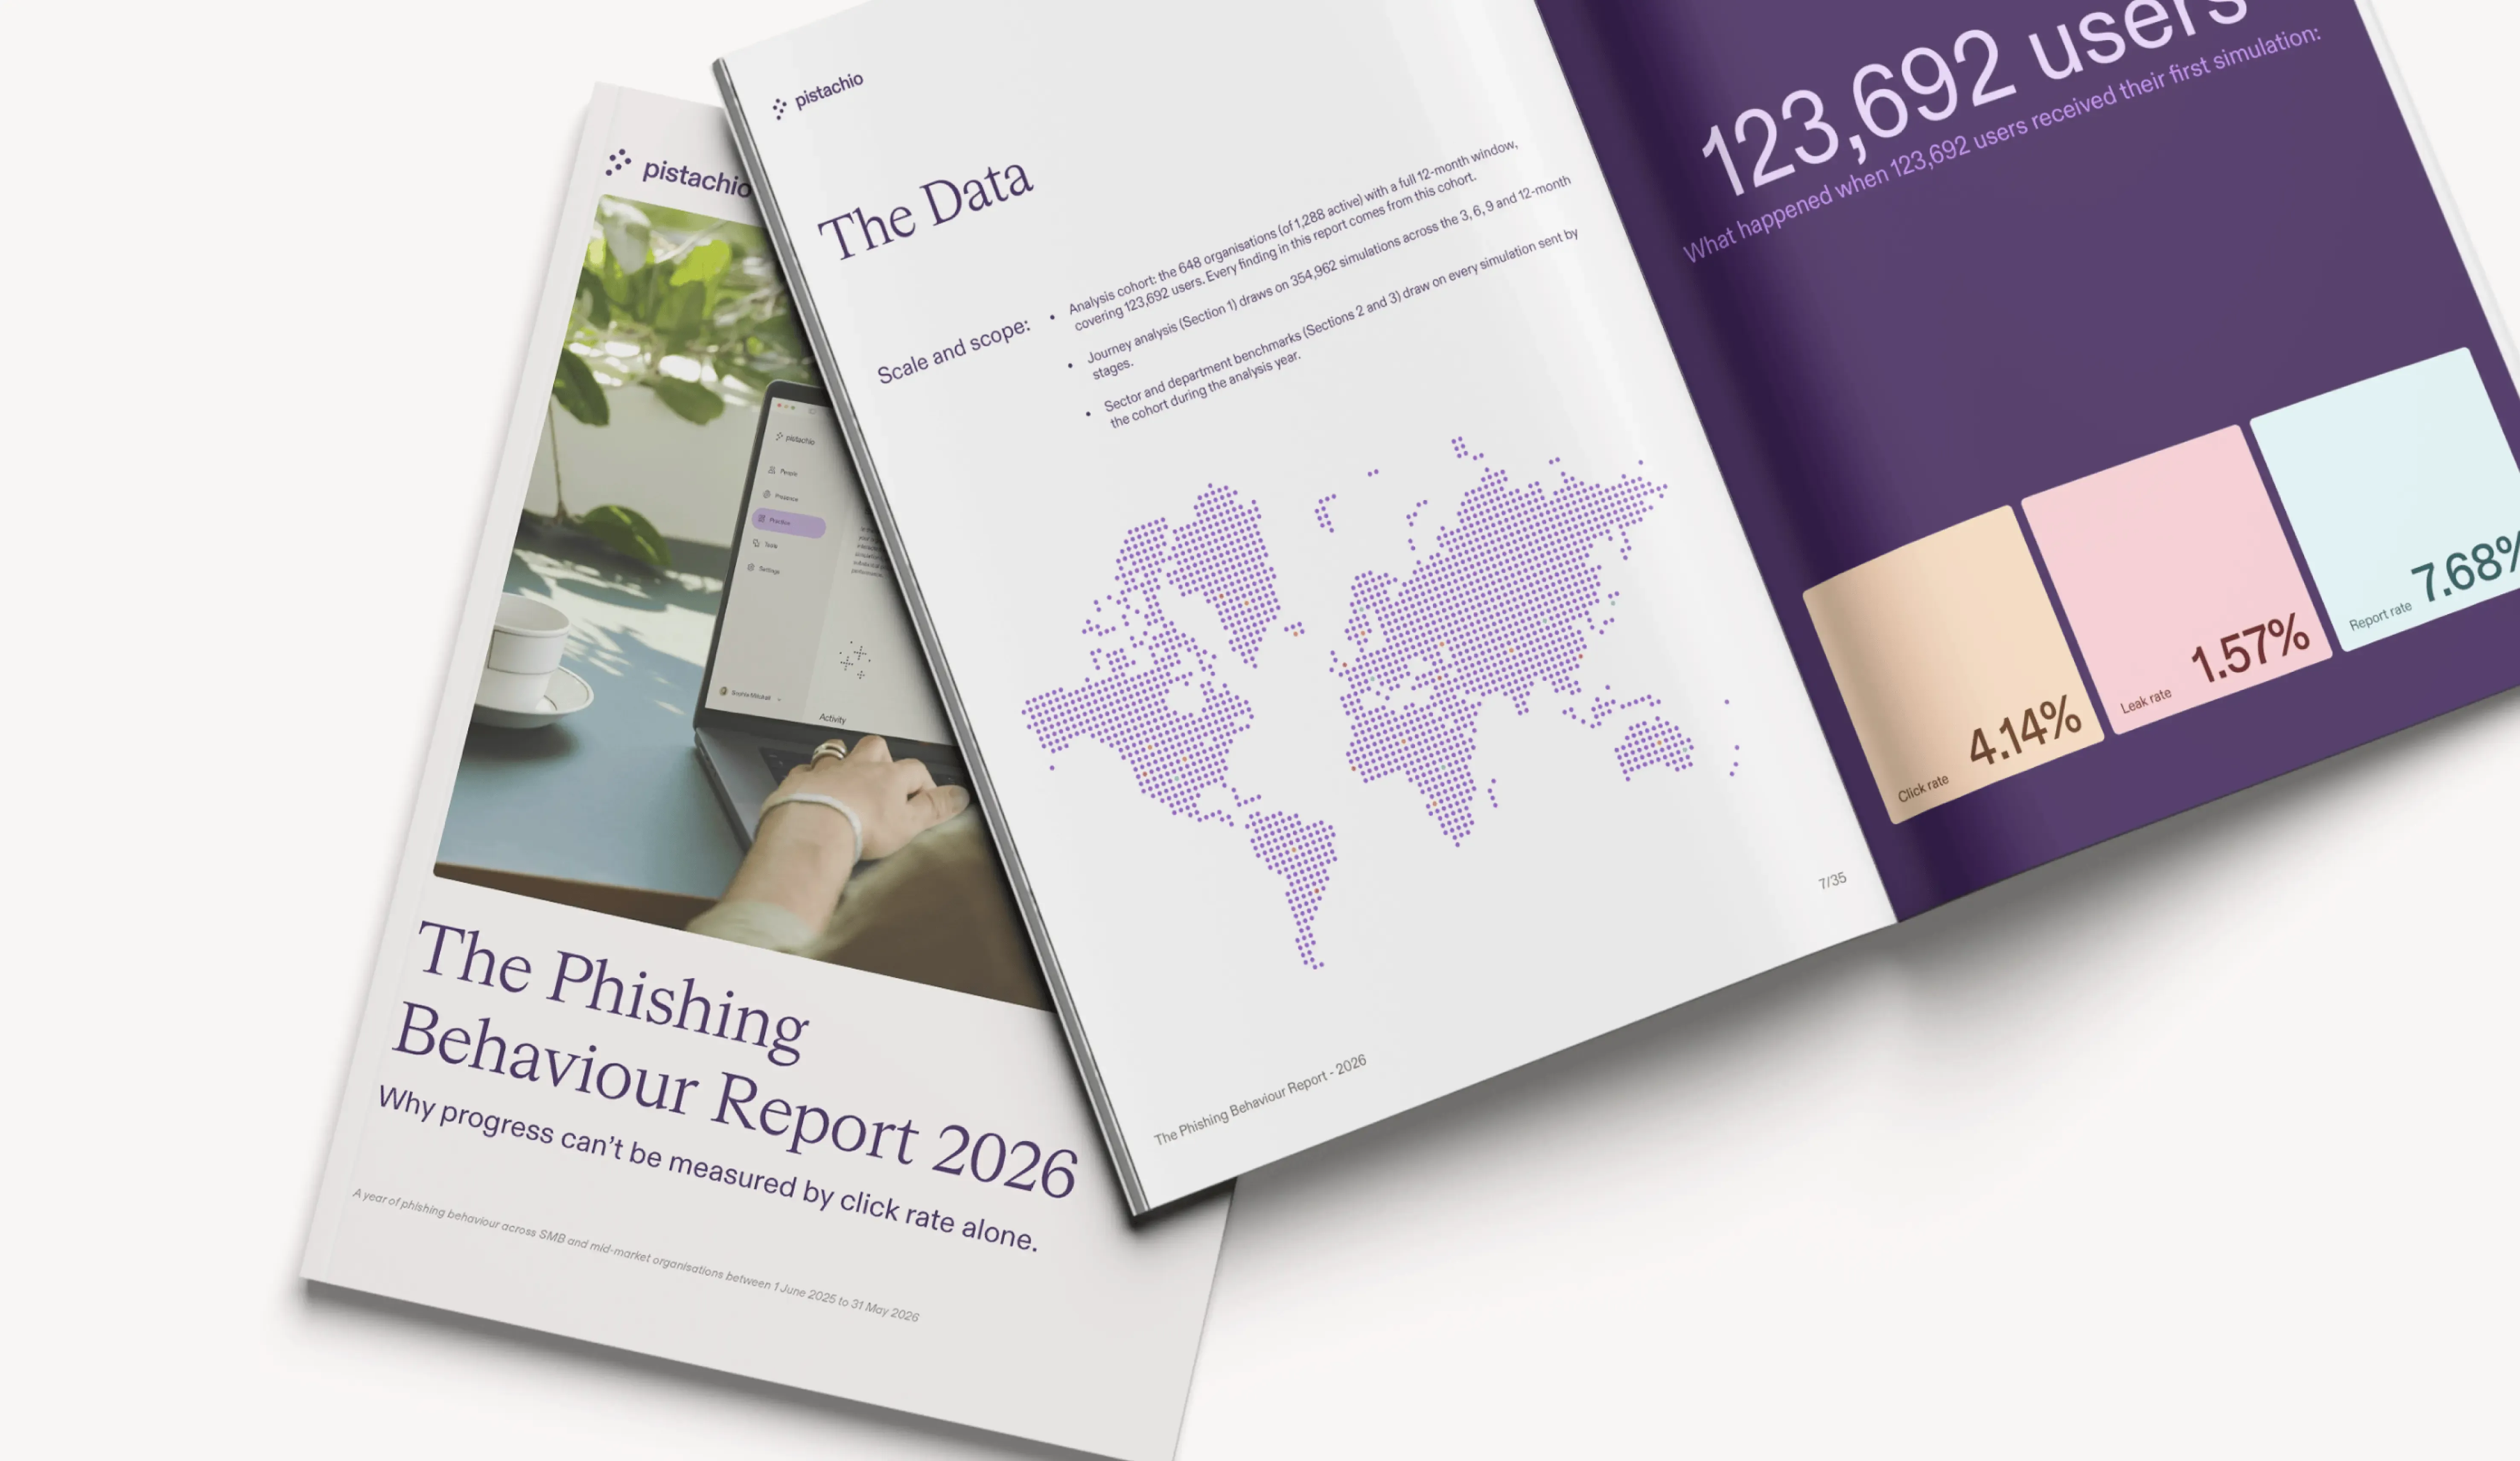
New report - A Year of Phishing Behaviour in SMB and Mid-Market Organisations
12-month journey analysis for over 120,000 users across 600+ organisations
We believe in a learn-by-doing approach over snooze-worthy videos.
Instead, Pistachio tailors real-world scenarios so your team can build their cyber skills in a safe environment.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Opinion Pieces
Article
Product
Attack Simulations
Phishing
Opinion Pieces
Article
Security Awareness
Tips
Attack Simulations
Cybersecurity 101
Article
Cybersecurity
Tech
Security Awareness

Cybersecurity 101
Article
Spoofing
Tips
Cyber Threats

Opinion Pieces
Article
Cybersecurity
Tech
DevOps
Opinion Pieces
Article
Phishing
Attack Simulations
AI

Opinion Pieces
Article
DevOps
Cyber Threats

Company Milestones
Article
Product
News