You've got enough on your plate. Human risk shouldn't add to it.
Reduce human risk without adding to your workload. Pistachio deploys in 10 minutes, then runs personalised security training and insider threat detection with minimal ongoing maintenance.

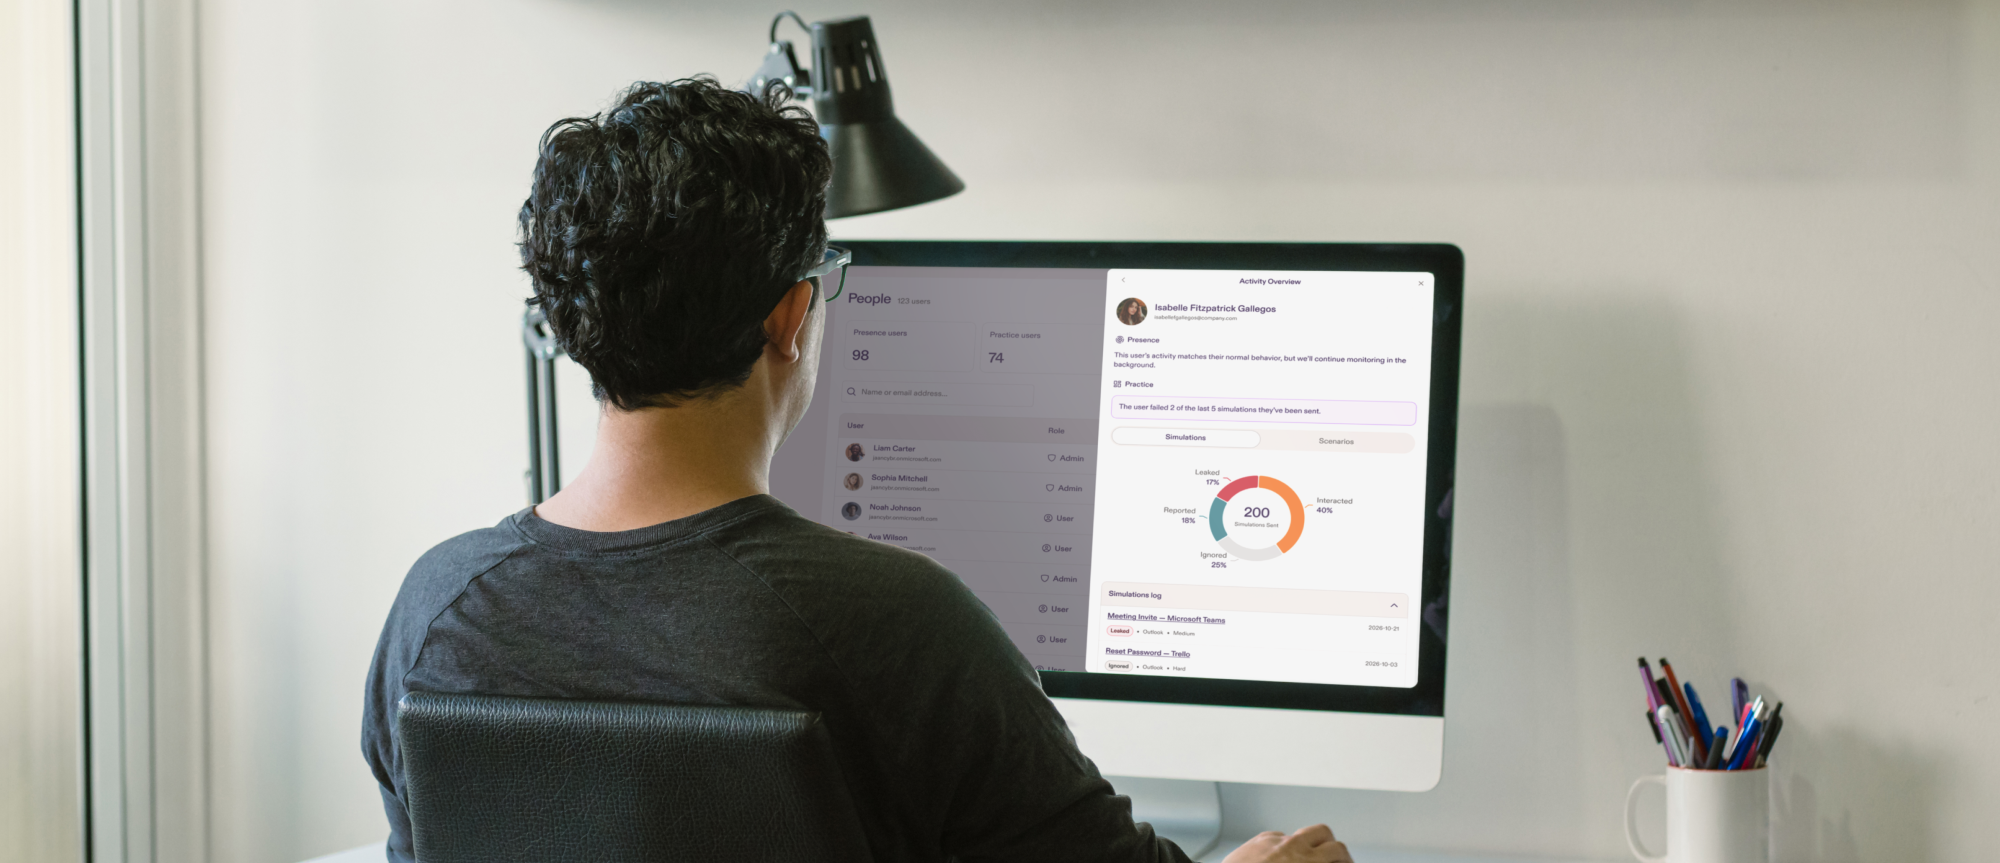


You’re already doing six jobs
Helpdesk, hardware, network, projects, security, and whatever lands on your desk next. Every new tool adds more to configure, monitor and maintain.
Most security software assumes someone has time to run it. Pistachio doesn’t.
Trusted by 1200+ customers & MSPs
















You’re already doing six jobs
Pistachio does the work for you

Live in 10 minutes
Connects with Microsoft Entra, no lengthy rollout project.

No manual admin
Automates the work that would otherwise sit with your team.

Automatic reporting
Board-ready reports that can be easily shared.

No specialist team
You login when you want to, rather than needing to.
Security you can be confident in

Your data stays in Europe. Everything is stored in Google Cloud in the EU and never leaves the EEA. Presence data stays in a single European data centre, with behavioural analysis running inside Google Cloud in Europe.

ISO 27001 certified. Independently audited every year.

We don't read your email. The mail permission lets us deliver and remove simulations. Nothing more. Pistachio doesn't read your emails and has no code that allows it to.
Security you can be confident in
How Pistachio reduces human risk

Security Awareness Training
Personalised and adaptive security awareness training that changes employee behaviour, making your people harder to exploit.

Trusted by lean teams across Europe
“We lacked confidence that employees would recognise today’s phishing threats or respond correctly. Since using the Pistachio platform, they are more attentive and proactive in identifying potential risks. The solution is easy to manage, quick to implement, and highly effective.
“The platform is easy to implement and provides clear insights into employee phishing awareness. Its bite-sized learning encourages participation, saves administration time, and allows us to focus more on real threat detection.”
“We were looking for a practical way to improve cybersecurity awareness across the organization. Pistachio made training simple and engaging, and we’ve seen a noticeable improvement in employee awareness with minimal effort.”
“Pistachio removed the burden of planning campaigns, collecting data, and evaluating results. The program challenges each employee at their own level and provides clear, simple reporting. Pistachio has streamlined our awareness training and strengthened our organization’s cybersecurity.”
“Our goal was to help employees better recognize phishing emails and avoid malicious links. Pistachio made this easy and engaging, and we’ve seen a clear improvement in detection, fewer clicks on phishing links, and reduced data disclosure. With minimal ongoing maintenance, it’s an effective and low-effort solution.”

“Within weeks, Presence had flagged several incidents that could have otherwise been missed, including employees forwarding company data to personal accounts during offboarding. The alerts are reliable and actionable, so we've built a full investigation process around them. Although I was skeptical at first, the value was obvious almost immediately.”
“Pistachio has reduced our manual workload to zero with its automated phishing simulations and in‑box delivery of scenario‑based trainings. This has allowed our team to dedicate time to other important security initiatives while Pistachio handles our Security Awareness program seamlessly.”
“Presence automatically detects suspicious behaviour and gives us the visibility we need without constant manual oversight. Within the first few weeks we were already seeing alerts that would have otherwise gone unnoticed as the system learns what is usual and unusual behaviour for our environment.”

“Before Pistachio, security awareness was something we could only offer to a few customers. Today it’s part of every managed service we deliver, and we haven’t had to grow the team to make that happen.”
Ready to reduce your human risk? Book your demo today.

“We lacked confidence that employees would recognise today’s phishing threats or respond correctly. Since using the Pistachio platform, they are more attentive and proactive in identifying potential risks. The solution is easy to manage, quick to implement, and highly effective.
“The platform is easy to implement and provides clear insights into employee phishing awareness. Its bite-sized learning encourages participation, saves administration time, and allows us to focus more on real threat detection.”
“We were looking for a practical way to improve cybersecurity awareness across the organization. Pistachio made training simple and engaging, and we’ve seen a noticeable improvement in employee awareness with minimal effort.”
“Pistachio removed the burden of planning campaigns, collecting data, and evaluating results. The program challenges each employee at their own level and provides clear, simple reporting. Pistachio has streamlined our awareness training and strengthened our organization’s cybersecurity.”
“Our goal was to help employees better recognize phishing emails and avoid malicious links. Pistachio made this easy and engaging, and we’ve seen a clear improvement in detection, fewer clicks on phishing links, and reduced data disclosure. With minimal ongoing maintenance, it’s an effective and low-effort solution.”
“Within weeks, Presence had flagged several incidents that could have otherwise been missed, including employees forwarding company data to personal accounts during offboarding. The alerts are reliable and actionable, so we've built a full investigation process around them. Although I was skeptical at first, the value was obvious almost immediately.”
“Pistachio has reduced our manual workload to zero with its automated phishing simulations and in‑box delivery of scenario‑based trainings. This has allowed our team to dedicate time to other important security initiatives while Pistachio handles our Security Awareness program seamlessly.”
“Presence automatically detects suspicious behaviour and gives us the visibility we need without constant manual oversight. Within the first few weeks we were already seeing alerts that would have otherwise gone unnoticed as the system learns what is usual and unusual behaviour for our environment.”
“Before Pistachio, security awareness was something we could only offer to a few customers. Today it’s part of every managed service we deliver, and we haven’t had to grow the team to make that happen.”
Fill out the form to book a demo:
Trusted by 1200+ customers & MSPs
Have a question?
Setup takes around 10 minutes. You log in with your Microsoft global admin credentials via single sign-on, create the security groups you need in Microsoft Entra ID, sync your organisation, and activate the platform with a single toggle. The system pulls in metadata (department, role, location, language) and starts working automatically, with machine learning beginning the moment you activate.
Yes. The trial runs for 14 days and gives you the full product, identical to the paid version. It begins as soon as you connect your Microsoft Entra ID, and the setup takes the same 10 minutes as a full deployment. The trial cannot be paused, and extensions beyond two weks are typically not offered, though you can discuss specific needs with your account executive. For Presence, add your whole organisation (end users won't know they're in a trial). For Practice, start with a pilot group and let them know they're taking part, since they'll receive training content, then expand later.
No. Pistachio does not read email content or document content, and has no capability to do so. For Practice, we only write simulations into mailboxes. For Presence, we analyse the same audit logs your IT admin could review manually (file names and locations, email subject lines and attachment names, login events, activity patterns), never the content itself.
Pistachio is designed to run automatically with no configuration on your side, and the permissions exist to make that possible. Pistachio requires four permissions from your Microsoft Entra tenant, granted via the OAuth 2.0 client credentials flow: User.Read lets users log in with their Microsoft accounts and gives access to basic profile information such as name. User.Read.All lets Pistachio read profile data (name, job title, department, location, email, language, photo) for licensed users only, to personalise simulations and surface relevant information to admins. Directory.Read.All lets Pistachio read group data and basic organisational information, such as your organisation's name and preferred language. Mail.ReadWrite is required to inject phishing simulations into mailboxes. Microsoft groups read and write permissions together under this single permission; the more precise permission for what we do would be Mail.Write, and we are actively lobbying Microsoft to split them. The specific endpoint we use ("Create mail in mail folder") only writes emails, it does not read them. Pistachio does not read your emails and has no code that would allow it to. Full detail is published at pistachioapp.com/permissions.
Practice includes two downloadable PDF reports generated on demand: a management report (an organisation-wide overview for leadership or IT) and a compliance report (the full training history, suitable for year-end audit and regulatory or insurance purposes). A CSV export of the raw data is also available, and all activity is captured from day one so historical data is always exportable. During a trial you get the same full dashboard access, including click rates, leak rates, interactions, and simulation difficulty levels.
Very little, and that is the point. Once activated, Pistachio runs on its own. Practice selects, personalises, and sends training automatically, and chases non-completions for you. Presence only alerts when something genuinely matters, filtering out the false positives that create noise. There are no rules to build, no campaigns to schedule, and no maintenance, so a small team gets enterprise-grade coverage without the workload.