Pistachio’s 2023 Year in Review
Find out about all of the changes the team made to Pistachio over the last five months as we close out the end of 2023.

Most companies write year-end reviews to highlight all of the great work they did that year. At Pistachio, our 2023 year-end review is actually an August-December review, as we only launched Pistachio in August. It doesn’t feel like it for us, but we really are only five months into this journey.
During those five months, we accomplished so much to make Pistachio into the best security awareness product on the market. And every new feature we built was made available to every single customer free of charge, because a core value at Pistachio is that we do not upsell new features. Buying Pistachio means buying the product you see today, with all of the improvements that will come tomorrow.
So what are those improvements? Let’s take a look.
Launch Day
We launched Pistachio at the start of August. At that time, all of the core parts of the product were in place. Our online signup, our free 14-day trial, the big “on button” that sets Pistachio into motion — all of that was there. And the core systems behind the scenes were all in place as well. We connect to your Microsoft Entra tenant (or Active Directory as it was then known), and utilize the data there to automatically send phishing simulations and training content to your employees based on a variety of factors, adjusting frequency, difficulty, types of content, and more.
The Pistachio we launched in August was on its own a great product that served its intended use case well, and customers flocked to it immediately. We had built the product that so many of our competitors claim to have: a training and attack platform that truly runs on autopilot. However, we knew there were so many more improvements to make.
Instant Training
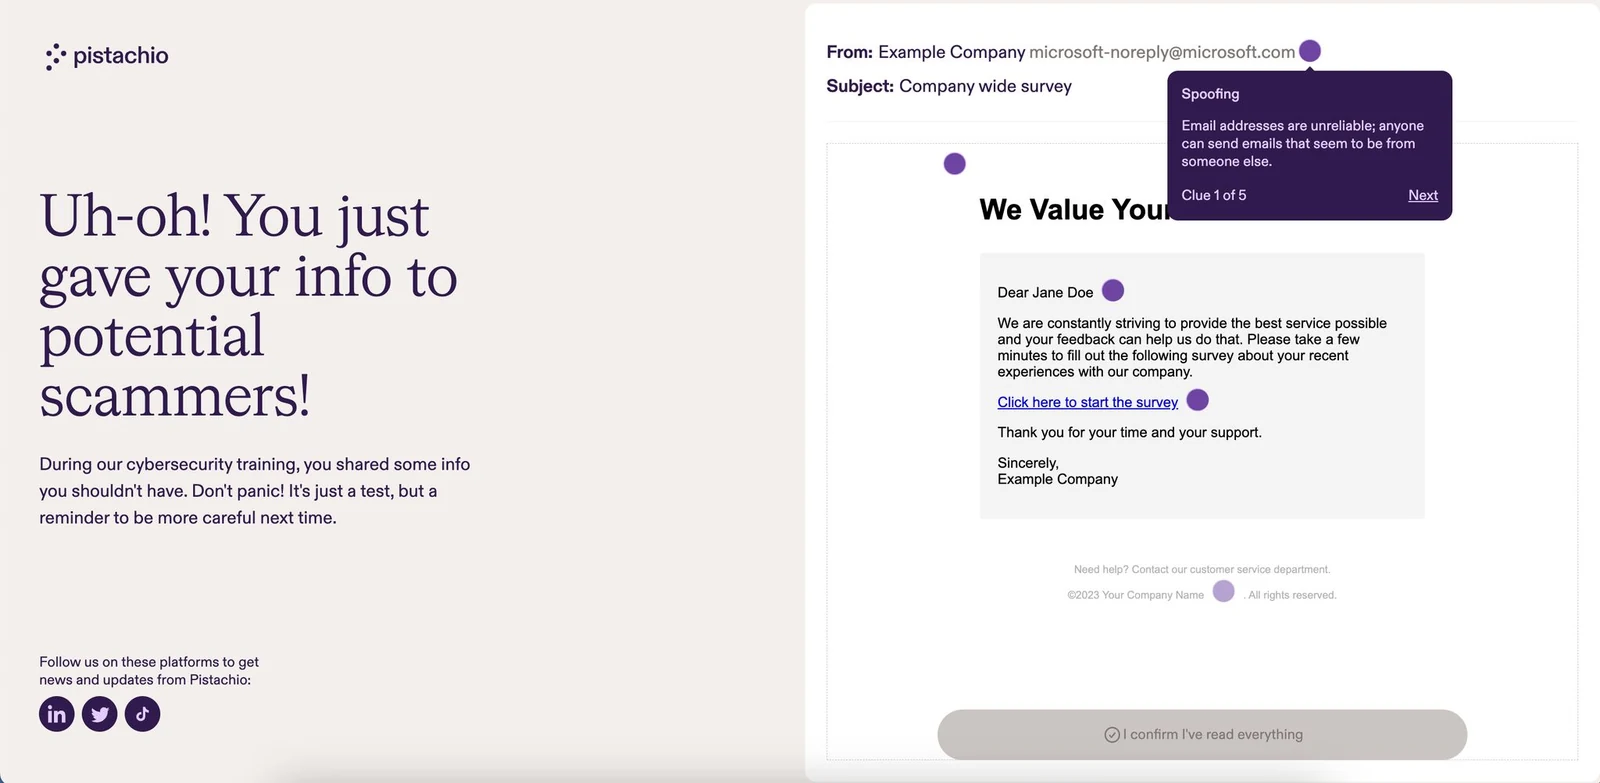
Our phishing simulations have always measured both if a user clicked a link in a phishing email, and if that user went on to leak his or her credentials. However, after leaking credentials, originally Pistachio simply sent the user to a page that explained that he or she fell for a phishing simulation. No further feedback was given.
We realized that was suboptimal, so we launched our “instant training” feature. After falling for a phishing simulation, a user is now shown a list of “clues” that he or she should have spotted in the original email. This gives immediate feedback on what to do differently next time. And we have found that this works! A user that falls for a phishing simulation is 50% less likely to click the next phishing simulation relative to someone who did not fall for the first simulation. This feature really makes people safer!
New Performance Page
When we first launched, the data we displayed to our customers was useful but still quite limited. We were doing some really cool things, but we weren’t showing all of that off. So, we reworked our performance page entirely. We made these changes progressively, rolling out a number of improvements:
1. Admins now have the ability to see a copy of the email we sent to each user, so they can see exactly what each person received.
2. We added two charts that show the distribution of our attacks and training according to categories and topics. This allows customers to see how Pistachio is covering a wide variety of areas, all done automatically.
3. At the top of the performance page, we now have a short text explaining how your organization is doing specifically. This makes it easy for admins to understand what Pistachio is doing and why without having to dig into the numbers.
4. The scatterplot of attacks was improved so as to give information about the difficulty to each attack being sent.
We also made a number of general design improvements at the same time, which are more subtle but should enhance the experience for our customers.

New Attacks (Including QR Code Phishing)
We have been adding new attacks at a steady rate since launching, and we now have over 300 different attacks in our system. These attacks cover a wide range of different tactics, softwares, languages, and locations.
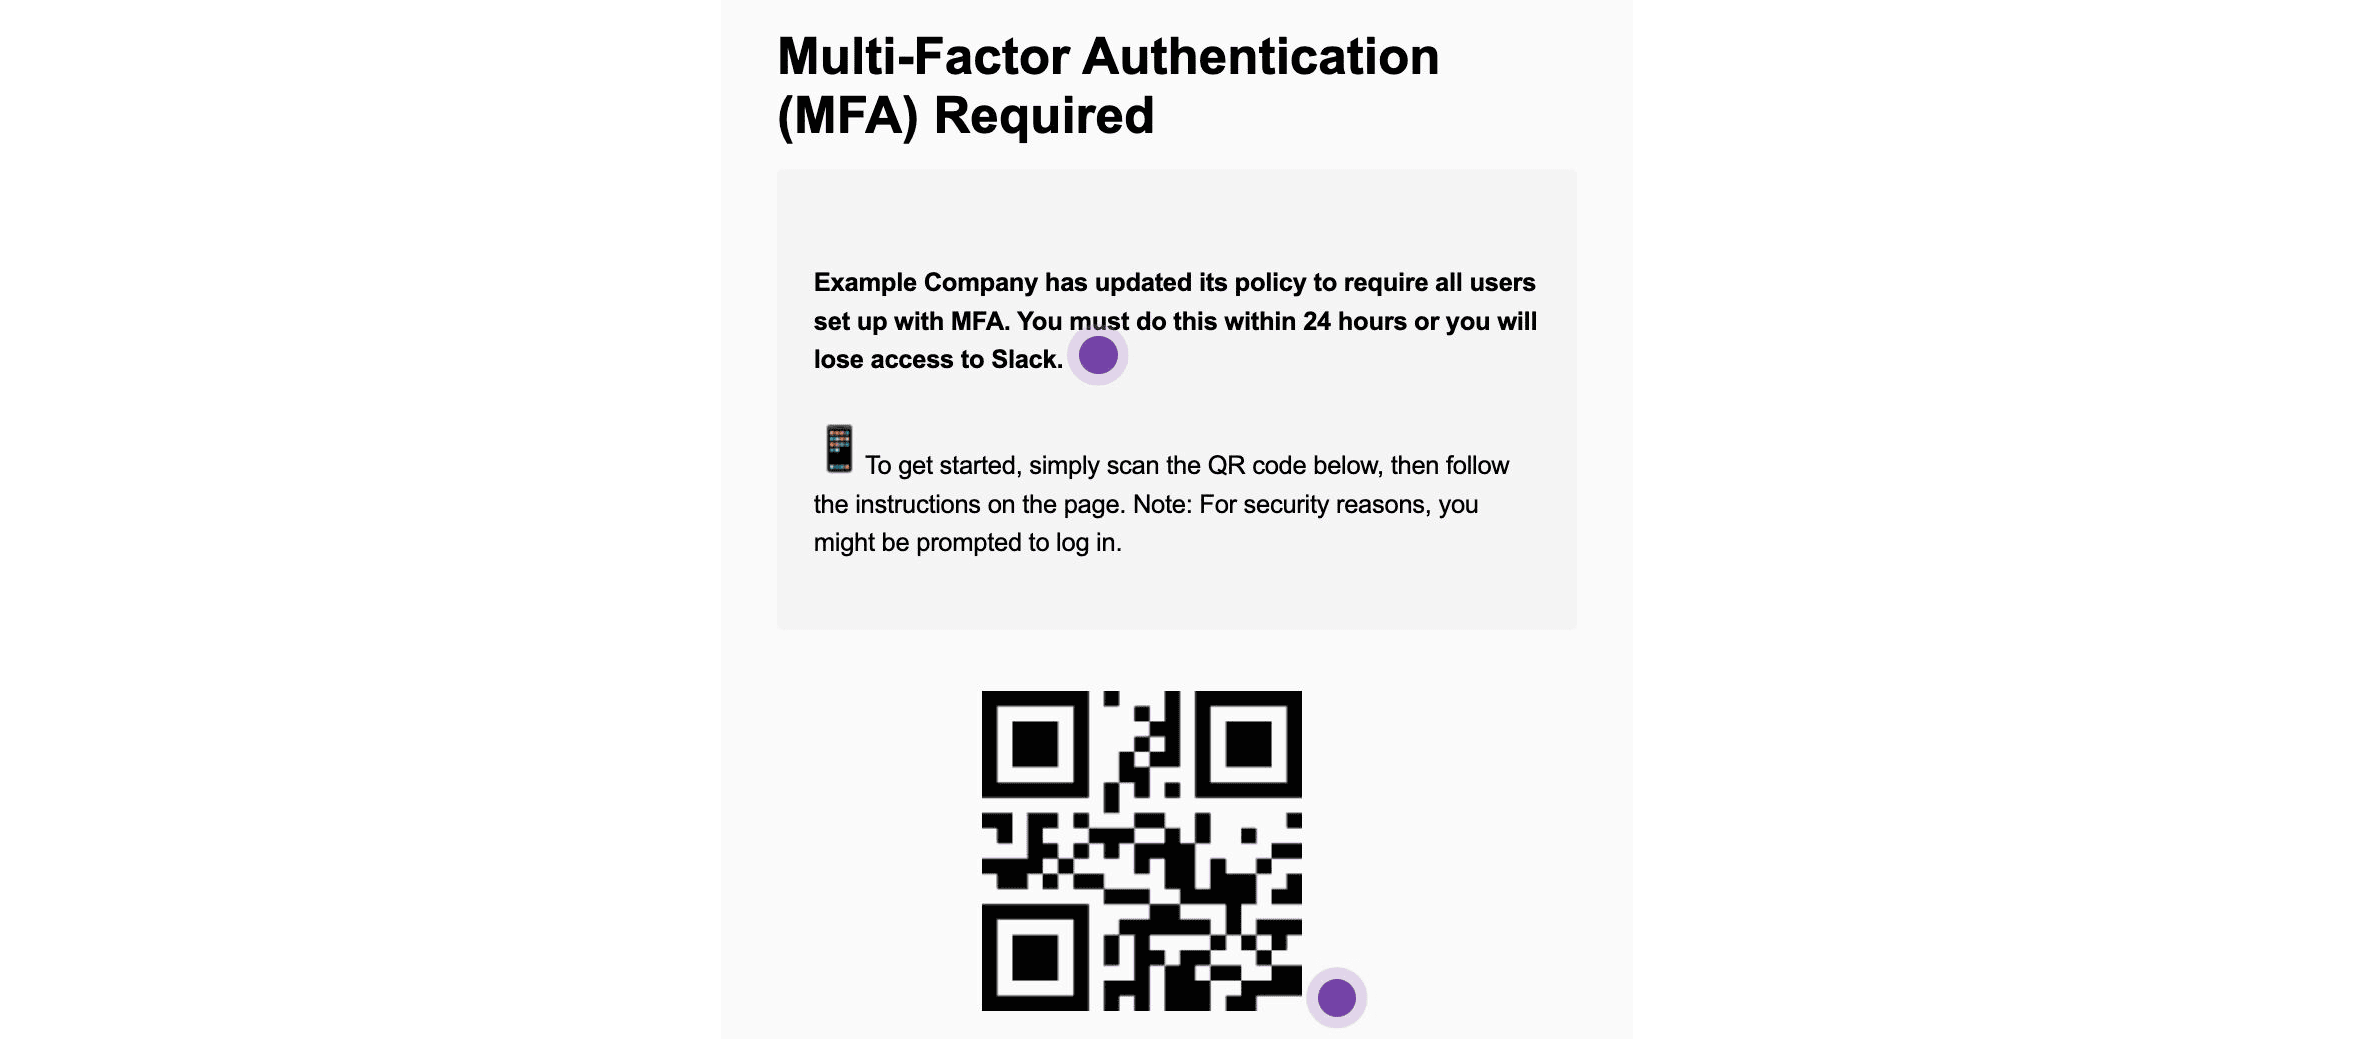
We also keep up with the latest threats, so when QR codes started appearing in phishing emails a few months back, we also added support for this into our system. Now, we have a handful of attacks that try to get people to scan a QR code rather than click a link.
Compliance and Management Reports
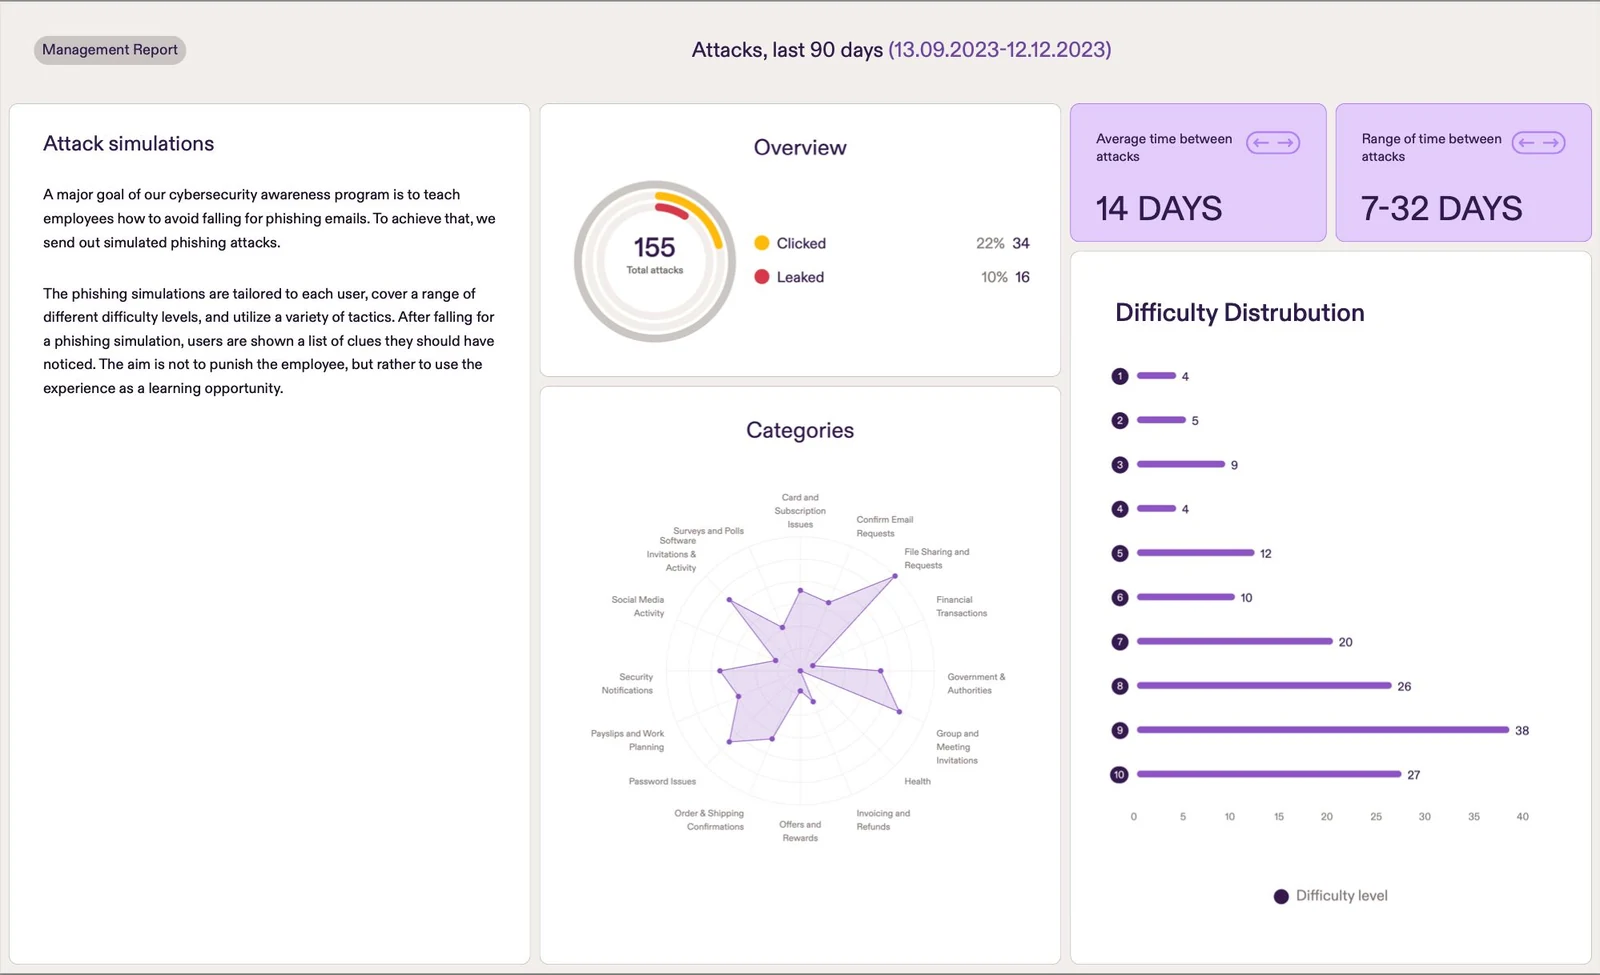
The number one feature request we received from customers over the last five months was a desire to have reports made for them. Some needed reports to satisfy auditors that they were taking security awareness seriously, while others needed reports to send to upper management. In both cases, we now have you covered.
The compliance report gives a short description of how Pistachio works, provides some high level statistics on what Pistachio is doing, and then displays a list of your users with the types of training and attack simulations they have each received.
The management report is a two-page document that you can add to presentations or include in your general reporting. It provides aggregated data on the training and attacks your employees are receiving, and how they are doing.
Behind the Scenes: Improved Personalization and Targeting
The biggest improvements, however, are hidden away behind the scenes. You can’t see them, not directly at least, but you do benefit from them. We have put a ton of work into improving the targeting of our attacks to ensure a more personalized and effective experience. This is, and always will be, the core of Pistachio.
To try to give you some insight into everything we have been doing, here are some of the changes we made:
1. Improved the way we match users with relevant content by looking more holistically at the information we have, rather than matching on individual pieces of information. This ensures that an IT Director that is a member of a Sales group is more likely to receive a simulation focused on Azure rather than HubSpot.
2. Created a system for ensuring that a given user receives a high degree of variety not just across categories and tactics, but also the software used.
3. Created a system for ensuring that a given organization also receives that variety, so that a group of users that all look very much alike initially still experience a wide range of attacks.
4. Adjusted the weightings that decide how our different scoring systems work together to ensure a better final result.
We also improved our internal systems for monitoring how these changes work to see whether we are moving in the right direction in making your organization more secure.
A Preview of 2024
It is very important to us that we don’t turn Pistachio into some overly complex monstrosity with a million buttons and toggles that no one uses. Almost all of the features added above operate automatically in the background so that each customer benefits without ever having to do a thing. The changes that do require interaction, like the compliance report and management report, are there for customers that need them but don’t distract from the product for those that don’t.
And that is how we plan on keeping it. Our main goal for 2024 is to improve the content (more and better attacks covering more software, locations, tactics, etc.), the targeting (better attack selection), and the overall experience for end users. Many of the changes will be subtle, but the impact will be large.
To all of our customers, we would like to say thank you. Thank you for believing in us, and believing in our product. Your support means the world to us.

We believe in a learn-by-doing approach over snooze-worthy videos.
Instead, Pistachio tailors real-world scenarios so your team can build their cyber skills in a safe environment.


Continue reading
Ready to reduce your human risk? Book your demo today.

“We lacked confidence that employees would recognise today’s phishing threats or respond correctly. Since using the Pistachio platform, they are more attentive and proactive in identifying potential risks. The solution is easy to manage, quick to implement, and highly effective.
“The platform is easy to implement and provides clear insights into employee phishing awareness. Its bite-sized learning encourages participation, saves administration time, and allows us to focus more on real threat detection.”
“We were looking for a practical way to improve cybersecurity awareness across the organization. Pistachio made training simple and engaging, and we’ve seen a noticeable improvement in employee awareness with minimal effort.”
“Pistachio removed the burden of planning campaigns, collecting data, and evaluating results. The program challenges each employee at their own level and provides clear, simple reporting. Pistachio has streamlined our awareness training and strengthened our organization’s cybersecurity.”
“Our goal was to help employees better recognize phishing emails and avoid malicious links. Pistachio made this easy and engaging, and we’ve seen a clear improvement in detection, fewer clicks on phishing links, and reduced data disclosure. With minimal ongoing maintenance, it’s an effective and low-effort solution.”
“Within weeks, Presence had flagged several incidents that could have otherwise been missed, including employees forwarding company data to personal accounts during offboarding. The alerts are reliable and actionable, so we've built a full investigation process around them. Although I was skeptical at first, the value was obvious almost immediately.”
“Pistachio has reduced our manual workload to zero with its automated phishing simulations and in‑box delivery of scenario‑based trainings. This has allowed our team to dedicate time to other important security initiatives while Pistachio handles our Security Awareness program seamlessly.”
“Presence automatically detects suspicious behaviour and gives us the visibility we need without constant manual oversight. Within the first few weeks we were already seeing alerts that would have otherwise gone unnoticed as the system learns what is usual and unusual behaviour for our environment.”
“Before Pistachio, security awareness was something we could only offer to a few customers. Today it’s part of every managed service we deliver, and we haven’t had to grow the team to make that happen.”
Fill out the form to book a demo:
Trusted by 1200+ customers & MSPs















