Detect the insider threats your security tools miss
Presence learns what normal looks like for every user and flags deviations automatically, with no analysts, rules or tuning.



Trusted by 1200+ customers & MSPs
















One of your biggest risks already has a login
Insider threats don't look suspicious.
It could be a leaver downloading files, a compromised account, or sensitive data sent somewhere it shouldn't be. Because it happens through legitimate accounts, it can be difficult to spot without constant monitoring.
of organisations had data incidents in the past 12 months
Fact
of security leaders lack full visibility into how people use sensitive data
Fact
Presence was built to manage this risk
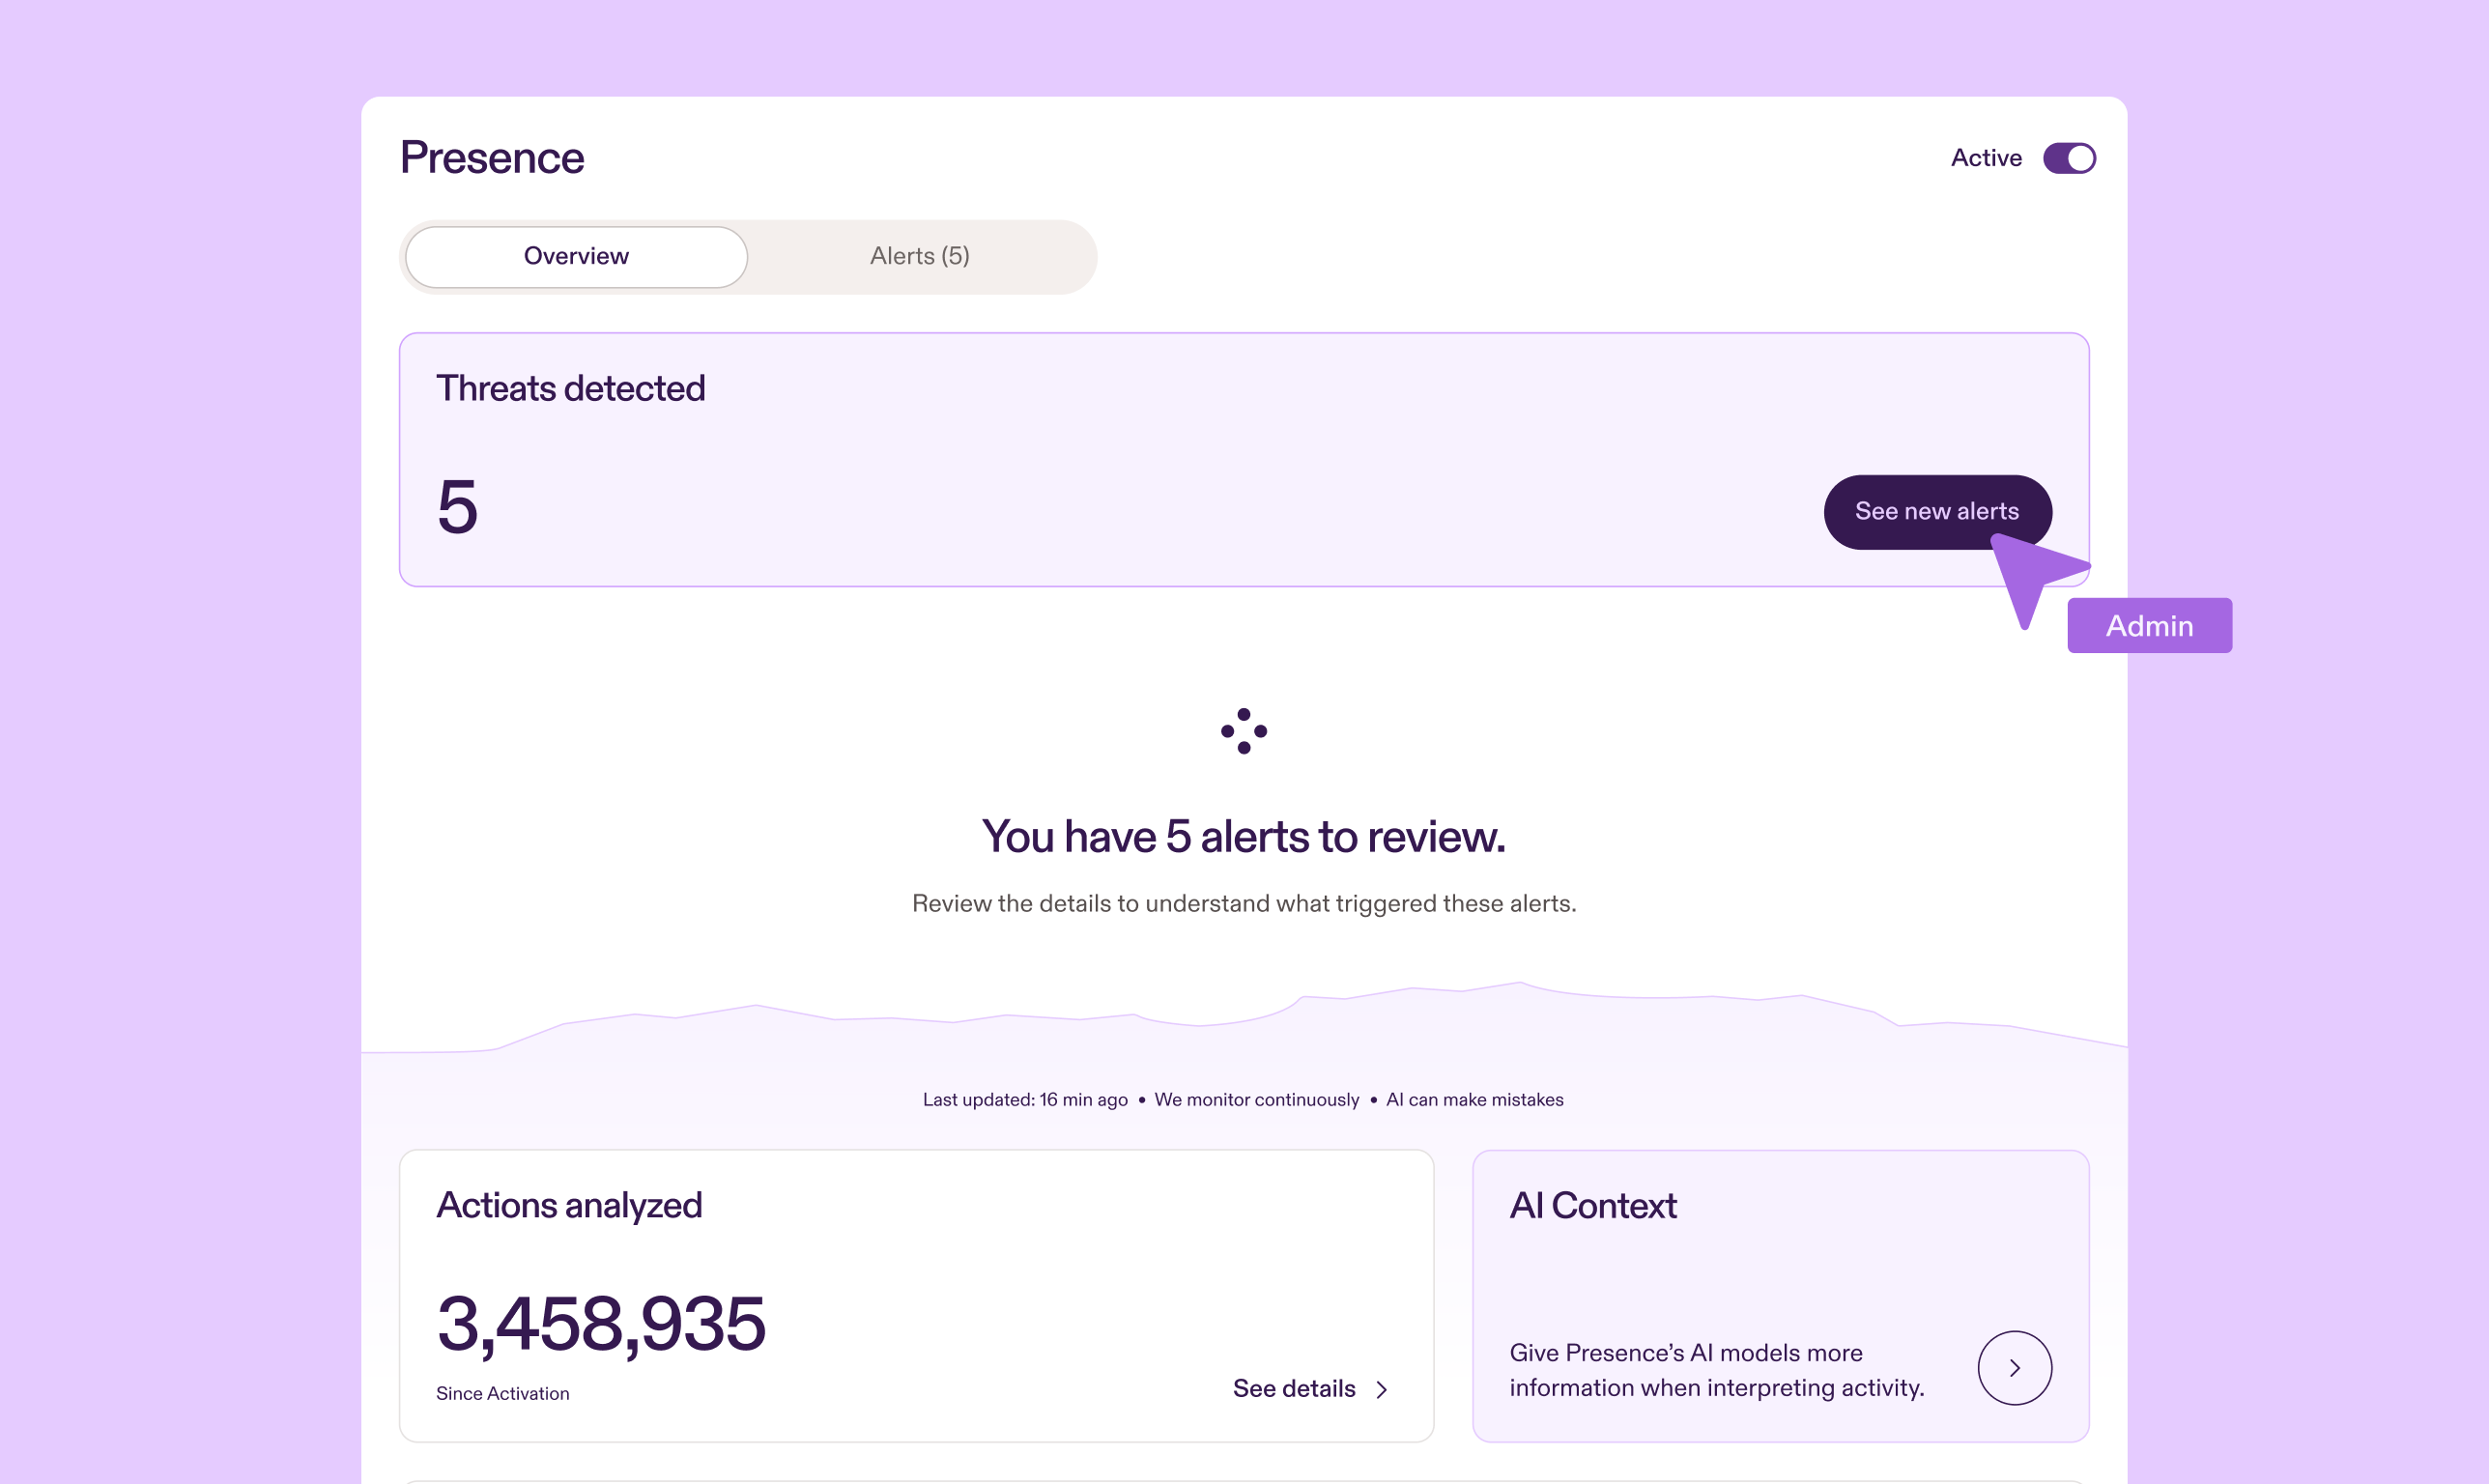
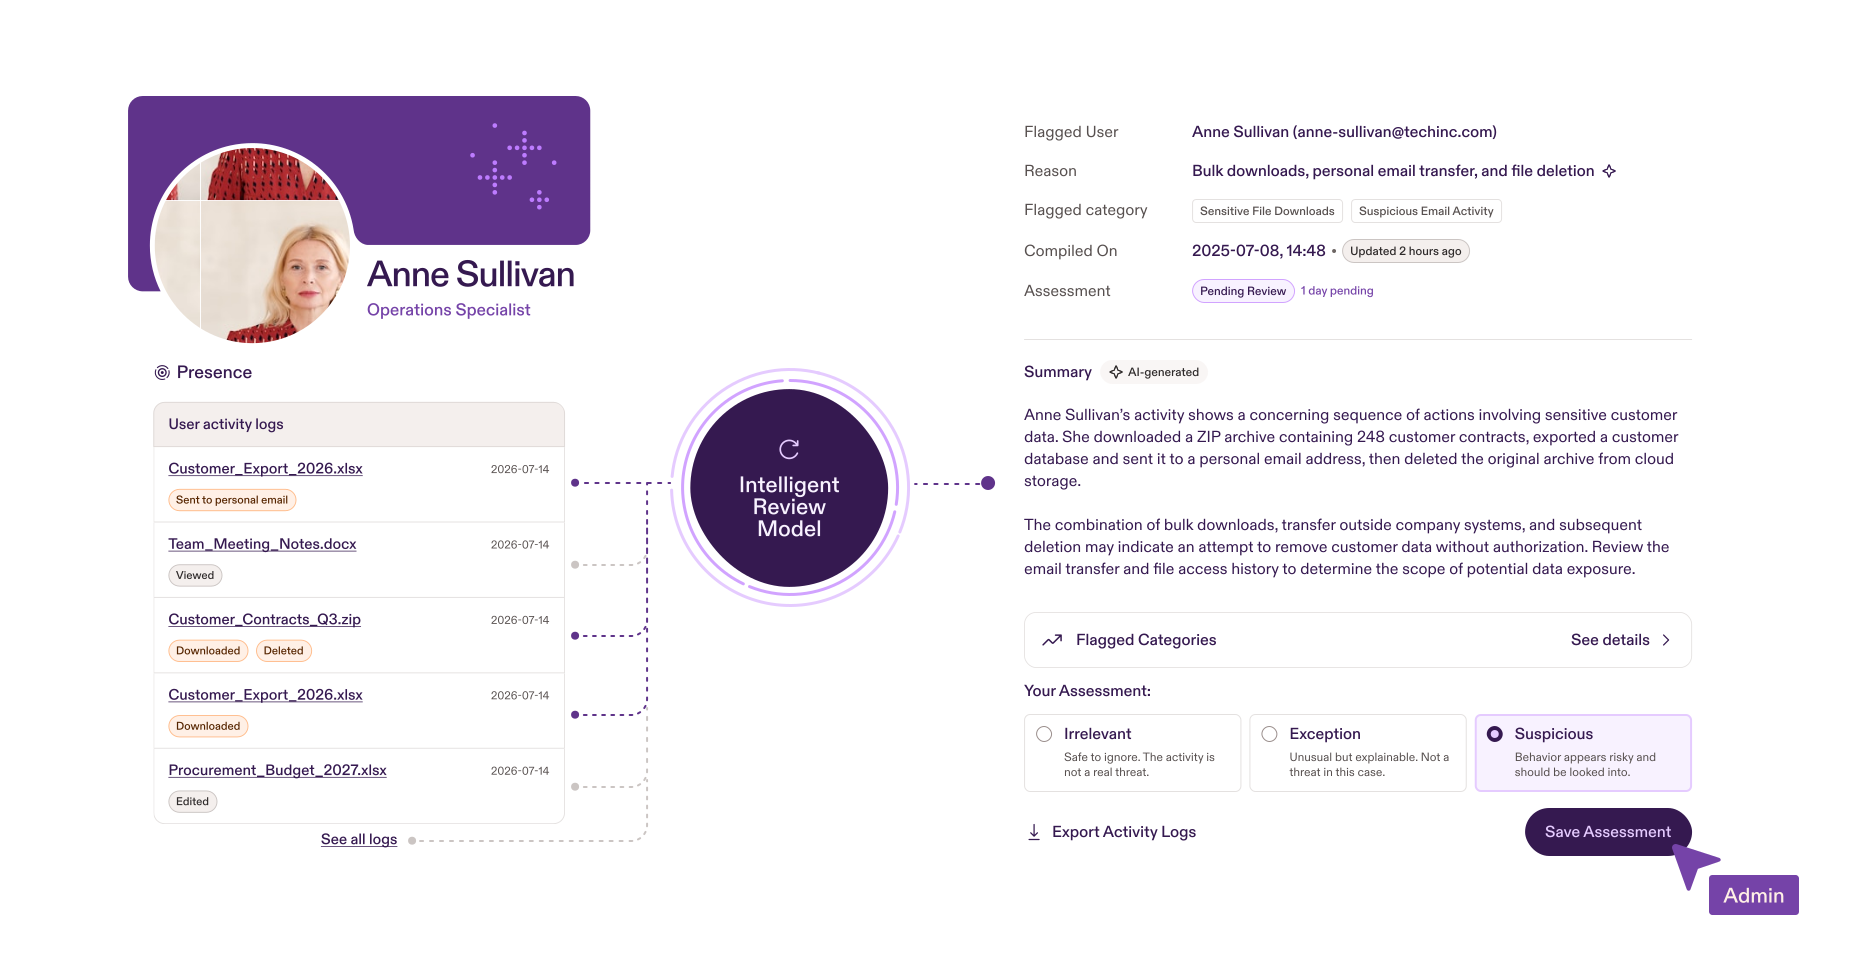
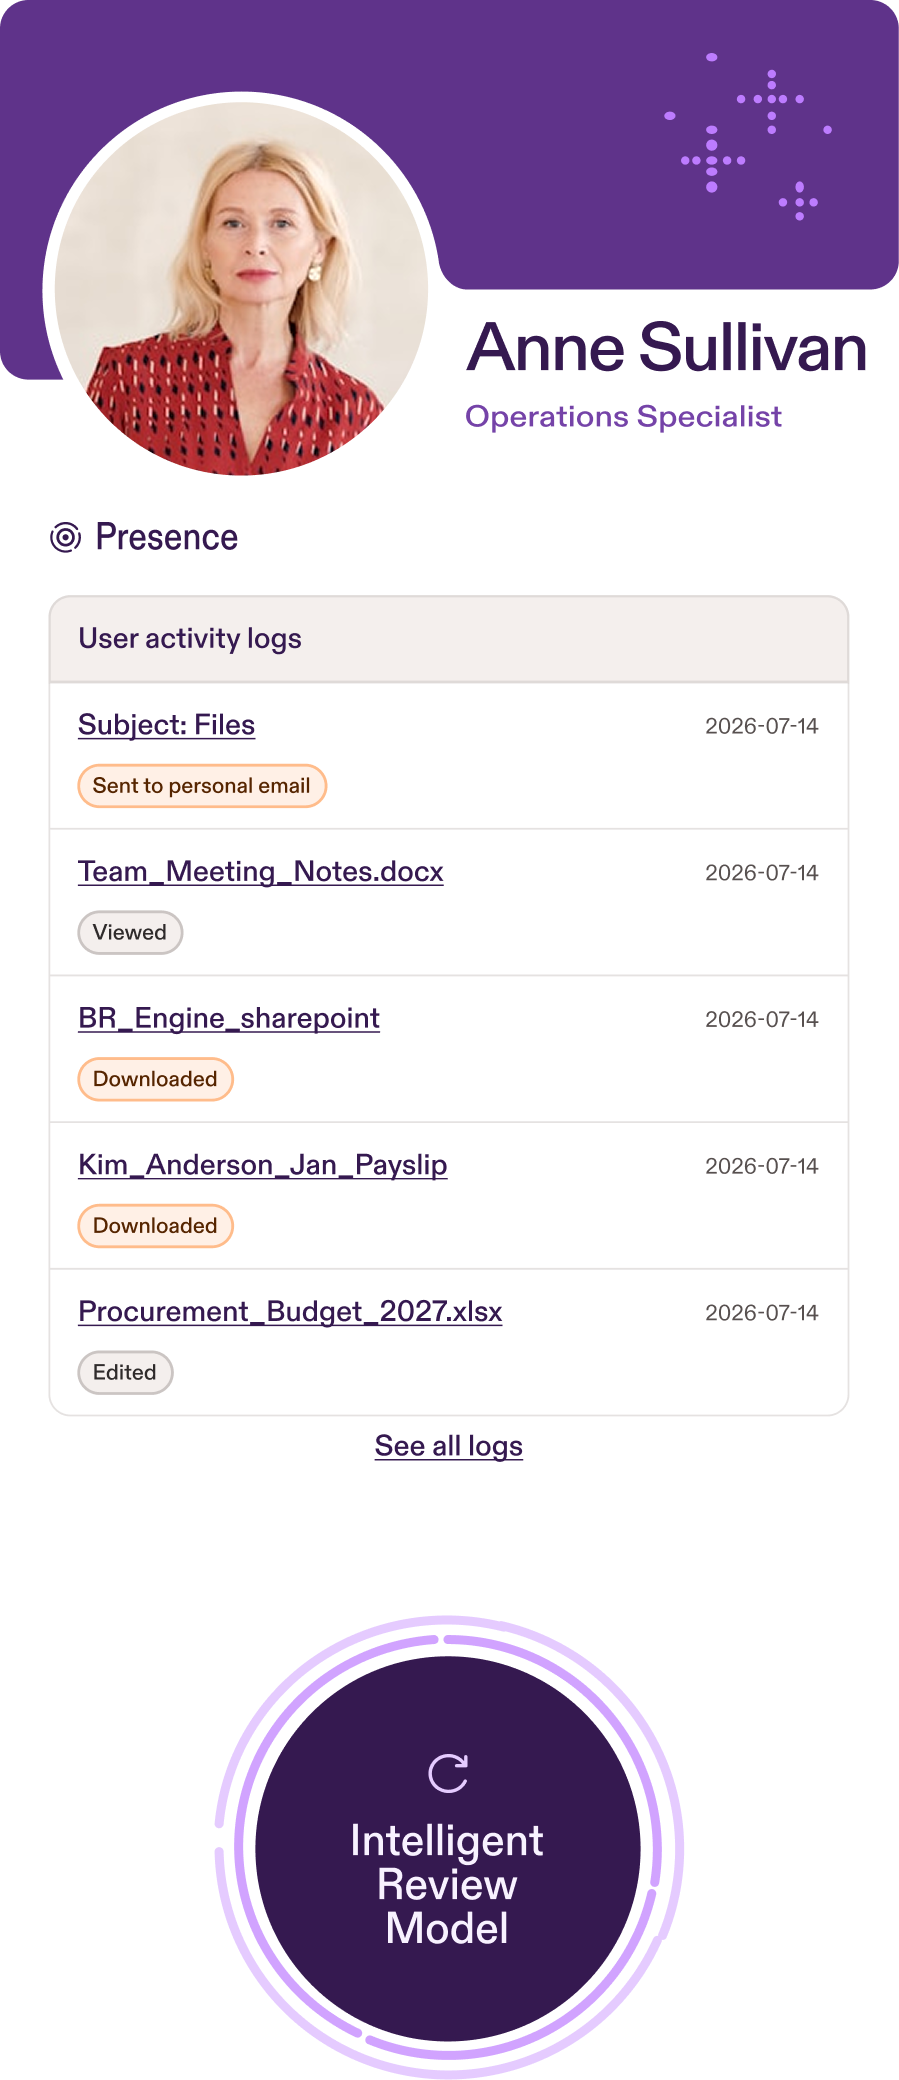
Presence watches the signals across your organisation, learns what's normal for each user, investigates what's not, and alerts when there's something that needs your attention.

“Within weeks, Presence had flagged several incidents that could have otherwise been missed, including employees forwarding company data to personal accounts during offboarding. The alerts are reliable and actionable, so we've built a full investigation process around them. Although I was skeptical at first, the value was obvious almost immediately.”
Insider threat detection for teams without a SOC

Behavioural AI
Baselines for every user, so deviations surface automatically, with no rules to write or maintain.

Contextual alerts
Each alert explains what happened, why it matters and what to do, so you're not drowning in false positives.

Low-risk events
Surfaces low-risk events that add up over time, like passwords in shared docs or unsafe downloads.

Canaries
Decoy emails planted in admin inboxes trigger the moment a compromised account takes the bait.

Privacy first
Presence flags risky activity, not everyday behaviour, and is privacy-first by design.
Built to help, not hinder, IT teams and MSPs
“We lacked confidence that employees would recognise today’s phishing threats or respond correctly. Since using the Pistachio platform, they are more attentive and proactive in identifying potential risks. The solution is easy to manage, quick to implement, and highly effective.
“The platform is easy to implement and provides clear insights into employee phishing awareness. Its bite-sized learning encourages participation, saves administration time, and allows us to focus more on real threat detection.”
“We were looking for a practical way to improve cybersecurity awareness across the organization. Pistachio made training simple and engaging, and we’ve seen a noticeable improvement in employee awareness with minimal effort.”
“Pistachio removed the burden of planning campaigns, collecting data, and evaluating results. The program challenges each employee at their own level and provides clear, simple reporting. Pistachio has streamlined our awareness training and strengthened our organization’s cybersecurity.”
“Our goal was to help employees better recognize phishing emails and avoid malicious links. Pistachio made this easy and engaging, and we’ve seen a clear improvement in detection, fewer clicks on phishing links, and reduced data disclosure. With minimal ongoing maintenance, it’s an effective and low-effort solution.”

“Within weeks, Presence had flagged several incidents that could have otherwise been missed, including employees forwarding company data to personal accounts during offboarding. The alerts are reliable and actionable, so we've built a full investigation process around them. Although I was skeptical at first, the value was obvious almost immediately.”
“Pistachio has reduced our manual workload to zero with its automated phishing simulations and in‑box delivery of scenario‑based trainings. This has allowed our team to dedicate time to other important security initiatives while Pistachio handles our Security Awareness program seamlessly.”
“Presence automatically detects suspicious behaviour and gives us the visibility we need without constant manual oversight. Within the first few weeks we were already seeing alerts that would have otherwise gone unnoticed as the system learns what is usual and unusual behaviour for our environment.”

“Before Pistachio, security awareness was something we could only offer to a few customers. Today it’s part of every managed service we deliver, and we haven’t had to grow the team to make that happen.”
Ready to reduce your human risk? Book your demo today.
“We lacked confidence that employees would recognise today’s phishing threats or respond correctly. Since using the Pistachio platform, they are more attentive and proactive in identifying potential risks. The solution is easy to manage, quick to implement, and highly effective.
“The platform is easy to implement and provides clear insights into employee phishing awareness. Its bite-sized learning encourages participation, saves administration time, and allows us to focus more on real threat detection.”
“We were looking for a practical way to improve cybersecurity awareness across the organization. Pistachio made training simple and engaging, and we’ve seen a noticeable improvement in employee awareness with minimal effort.”
“Pistachio removed the burden of planning campaigns, collecting data, and evaluating results. The program challenges each employee at their own level and provides clear, simple reporting. Pistachio has streamlined our awareness training and strengthened our organization’s cybersecurity.”
“Our goal was to help employees better recognize phishing emails and avoid malicious links. Pistachio made this easy and engaging, and we’ve seen a clear improvement in detection, fewer clicks on phishing links, and reduced data disclosure. With minimal ongoing maintenance, it’s an effective and low-effort solution.”
“Within weeks, Presence had flagged several incidents that could have otherwise been missed, including employees forwarding company data to personal accounts during offboarding. The alerts are reliable and actionable, so we've built a full investigation process around them. Although I was skeptical at first, the value was obvious almost immediately.”
“Pistachio has reduced our manual workload to zero with its automated phishing simulations and in‑box delivery of scenario‑based trainings. This has allowed our team to dedicate time to other important security initiatives while Pistachio handles our Security Awareness program seamlessly.”
“Presence automatically detects suspicious behaviour and gives us the visibility we need without constant manual oversight. Within the first few weeks we were already seeing alerts that would have otherwise gone unnoticed as the system learns what is usual and unusual behaviour for our environment.”
“Before Pistachio, security awareness was something we could only offer to a few customers. Today it’s part of every managed service we deliver, and we haven’t had to grow the team to make that happen.”
Fill out the form to book a demo:
Trusted by 1200+ customers & MSPs
Have a question about Presence?
Presence is an AI-driven insider threat detection tool. It connects to your cloud environment in minutes and uses AI to form a total assessment of a person's behaviour before deciding whether they're a threat, rather than firing on simple rules. That means less time spent on false positives and configuration, and fewer real threats missed because they fell outside a rule.
Presence works from Microsoft 365 audit logs, including email activity, file downloads, SharePoint and OneDrive access, login events, and unusual working hours. It reads metadata only (document names and locations, email subject lines and attachment names, login events, activity patterns) and never email or document content. For example, if someone in marketing suddenly accesses finance documents, that can trigger an alert without Presence ever opening the files.
No. Presence is entirely cloud-based and works from audit logs. You grant permissions and turn it on.
Presence works with standard Microsoft 365 licences, including Business Standard, Business Premium, E3, and E5. You do not need premium licences. The only requirements are Microsoft Entra ID and cloud-based mailboxes in Microsoft 365. If you already use Microsoft Purview for data loss prevention, your existing P1 licences are sufficient, with no upgrade to P2 needed.
Unlike Purview, Presence needs no manual rule setup or ongoing maintenance. It uses AI to build an individual baseline for each user and gives context-driven alerts rather than a flood of false positives, and setup takes minutes rather than months.
An alert appears in the Pistachio platform, and because genuine alerts are rare, an email also goes to a designated admin for every new alert so nothing is missed. Each alert includes the flagged user's details, clear reasoning for why the behaviour is unusual, a breakdown of specific findings (for example unusual working hours, high download volume, sensitive file downloads, or suspicious email activity), and the option to download the exact underlying audit logs as a CSV. Presence takes no automated action: a person on your side reviews the alert and decides how to proceed.