Getting Your Security Awareness Training Approved by Finance
How to build a stronger business case for security awareness training using industry risk, compliance requirements, internal data and measurable results.
Cyberattacks make the news most weeks. So, it seems an obvious "yes" when it comes to allocating budget to security awareness training. Everyone in the approval chain already knows the risk, the IT team doesn't have to convince them of that. And yet it is consistently the line item that gets pushed to next quarter.
Finance rarely rejects the investment because they don't believe there's a risk. It rejects it because the business case often leans on extremes. A mid-sized manufacturer doesn't see itself in a £300 million cyber attack1.
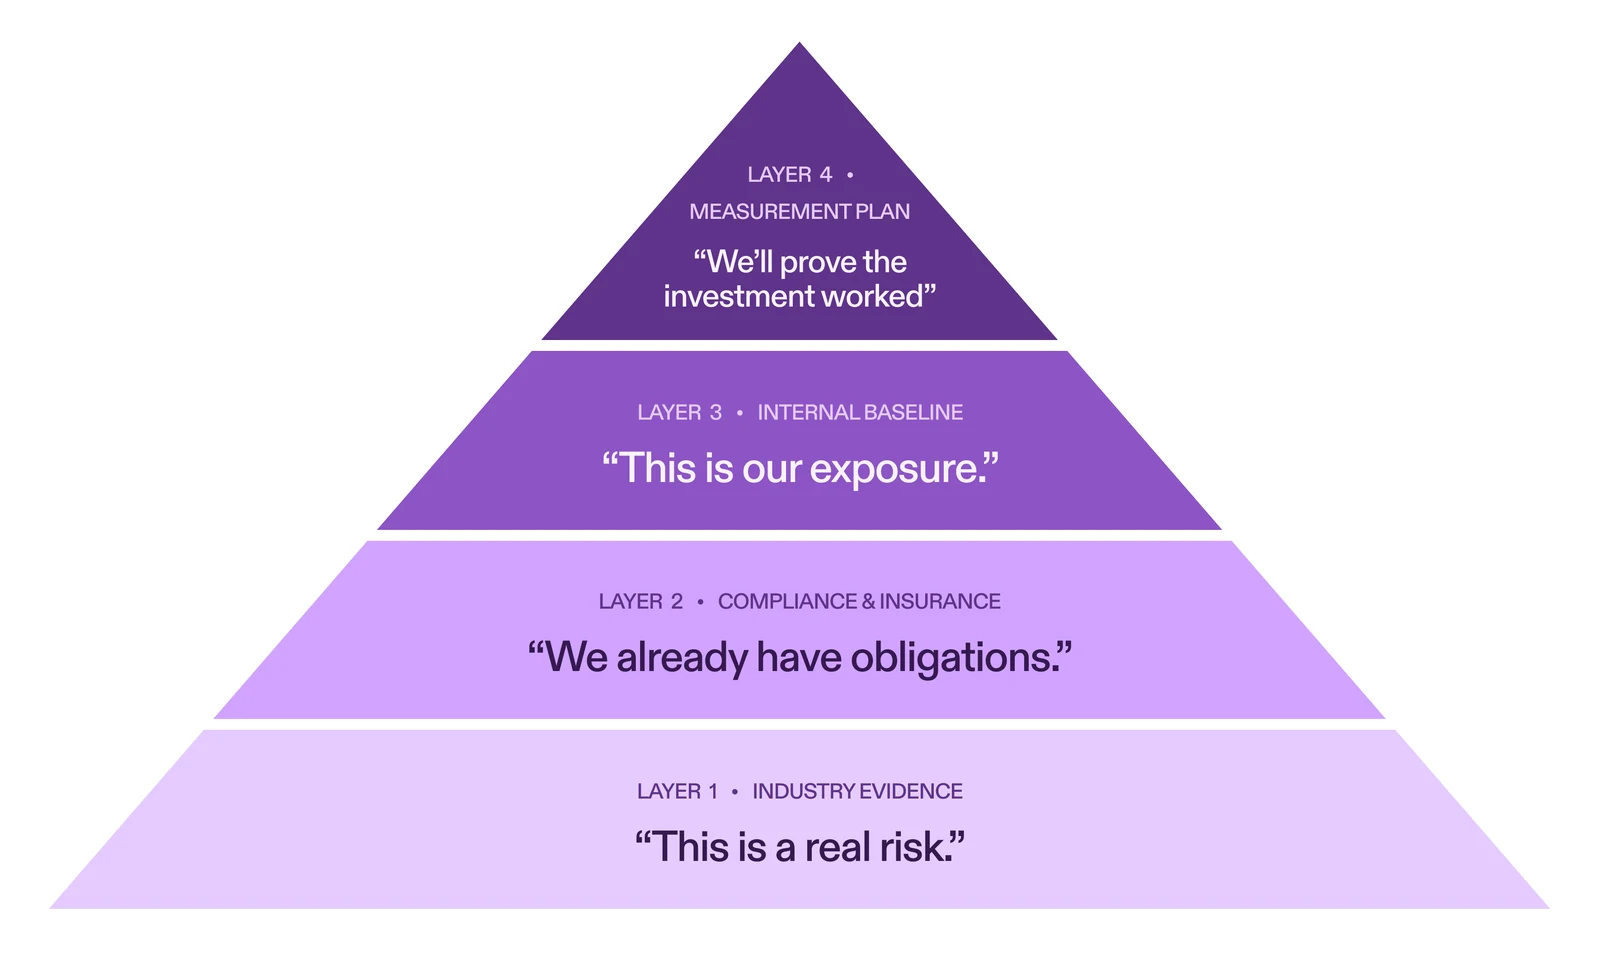
The business case isn't built on one statistic. It needs four evidence layers.
In conversations with IT managers, a familiar pattern comes up: a training line item gets raised, agreed as important, then pushed down the list again next quarter, not because anyone disputes the risk, but because the case never has enough behind it to outweigh whatever else is competing for the budget.
A breach headline is memorable, but it isn't a business case on its own. What moves a request through finance is layering four kinds of evidence, so no single figure has to carry the argument: what the industry already knows, what compliance and insurance already require, what a business's own data shows, and how success will be measured once the budget is spent. Each layer answers a different objection.
Together they become much harder to dismiss than any single statistic.
Layer one: what the industry already knows
Most breach cost headlines are pulled toward the large enterprise and US incidents that dominate the averages, which is exactly why they're easy for a mid-sized business to dismiss.
What holds regardless of company size is the mechanism behind the cost: phishing remains the most common way attackers get in, and breaches involving the human element, error, stolen credentials or social engineering, now account for the majority of incidents tracked industry-wide2. Even accounting for that skew, the global average cost of a data breach still reached $4.99 million in 2026, a 12% rise on the year before3.
Different industries also carry different specific risk, and naming it makes the number land. Healthcare breaches average $6.6 million and financial services $6.3 million, driven by regulatory exposure and the sensitivity of the data itself, while the industrial sector, the category that includes manufacturing, averages $5.5 million, driven more by operational downtime than data loss4. Matching the statistic to the reader's own sector is what makes this layer credible.
This layer establishes that the risk is real, quantified and, once narrowed to sector, recognisable.
Layer two: what compliance and insurance already require
For organisations in scope of NIS2, there's a number worth putting in front of finance directly: fines of up to €10 million or 2% of global annual turnover for essential entities, and up to €7 million or 1.4% for important entities, whichever is higher5. NIS2 also introduces personal liability for management in cases of proven negligence, which tends to get a business case read by people who wouldn't otherwise open it6.
Cyber insurers have moved the same way. Renewal terms now expect documented, continuous training with phishing simulation records, not a single annual completion certificate, and providers that can't show this are priced less favourably at renewal7.
That renewal date often lands whether the business is ready or not, making it one of the more reliable moments to attach a training request to. This layer turns the risk into an obligation the business already carries.
Layer three: what a business's own data shows
The first two layers are borrowed evidence. This one belongs to the business asking for budget, which is why it tends to do the most work in the room.
A baseline phishing simulation before the budget conversation turns "this could happen to us" into a number the business can discuss. Pistachio's 14-day free trial gives IT teams a way to generate that number without needing sign-off first, often the piece of evidence that gets a stalled request moving.
Layer four: how success will be measured
No marketing manager would submit a budget request for new software without a clear view of how ROI gets tracked. Security awareness training is often the exception, approved on faith and never checked again, which is exactly why finance hesitates to sign off on it in the first place.
This layer closes that gap before finance raises it. It commits upfront to which metrics will be reported, phishing click rate, leak rate, reporting rate and risk trends rather than course completion, and how often.
It's the same approach that let the University of St Andrews prove its compromise rate had dropped from 20-25% to 1-2% after adopting continuous, automated training8. Attaching that report to the request, before the money is spent rather than after, is what turns a one-off approval into a budget line that gets renewed next year.
Creating your business case
The industry data, the compliance exposure, the baseline number and the measurement plan are already there, quantified by parties finance already trusts. Layered together, they turn a training request from a line item that's easy to defer into one finance can justify to the board.
Practice from Pistachio is built around that argument:
Evidence for auditors and insurers. Automatically produces the records needed for NIS2, ISO 27001 and Cyber Essentials, making compliance easier to demonstrate at renewal or audit.
A measurable reduction in human risk. Establishes a baseline through real phishing simulations and tracks change over time, giving finance something more meaningful than a completion percentage.
Predictable operational cost. Runs automatically after a 10-minute deployment via Microsoft Entra, so ongoing administration doesn't quietly add to the total cost of ownership.
Board-ready reporting. Shows trends in phishing susceptibility and reporting behaviour, the kind of evidence a budget holder can put in front of their own board.
A request built on layered evidence, with a measurement plan attached from the start, is the one that gets approved and the one that gets renewed.
See how Practice helps you build a business case finance can approve, and prove the results afterwards.
Start your free trial or email contact@pistachioapp.com to book your 15-minute demo.
Infosecurity Magazine, "M&S Braces for £300 Million Cyber-Attack Costs," 2025↩
[Verizon, 2026 Data Breach Investigations Report.]↩
IBM, Cost of a Data Breach Report 2026, as reported by The HIPAA Journal, "Global Data Breach Cost Rises 12% to Almost $5 Million," July 29, 2026.↩
IBM, Cost of a Data Breach Report 2026, as reported by Infosecurity Magazine, "The Average Cost of a Data Breach Rises to $5 Million," July 29, 2026.↩
NIS2Directive.eu, "NIS2 Fines & Consequences," accessed August 2026.↩
NIS2Directive.eu, "NIS2 Fines & Consequences," accessed August 2026.↩
Core Managed, "Cyber Insurance Requirements Are Changing: What Your Renewal Will Look Like in 2026," 2026.↩
[University of St Andrews customer results, Pistachio case study.]↩

We believe in a learn-by-doing approach over snooze-worthy videos.
Instead, Pistachio tailors real-world scenarios so your team can build their cyber skills in a safe environment.


Continue reading
Ready to reduce your human risk? Book your demo today.

“We lacked confidence that employees would recognise today’s phishing threats or respond correctly. Since using the Pistachio platform, they are more attentive and proactive in identifying potential risks. The solution is easy to manage, quick to implement, and highly effective.
“The platform is easy to implement and provides clear insights into employee phishing awareness. Its bite-sized learning encourages participation, saves administration time, and allows us to focus more on real threat detection.”
“We were looking for a practical way to improve cybersecurity awareness across the organization. Pistachio made training simple and engaging, and we’ve seen a noticeable improvement in employee awareness with minimal effort.”
“Pistachio removed the burden of planning campaigns, collecting data, and evaluating results. The program challenges each employee at their own level and provides clear, simple reporting. Pistachio has streamlined our awareness training and strengthened our organization’s cybersecurity.”
“Our goal was to help employees better recognize phishing emails and avoid malicious links. Pistachio made this easy and engaging, and we’ve seen a clear improvement in detection, fewer clicks on phishing links, and reduced data disclosure. With minimal ongoing maintenance, it’s an effective and low-effort solution.”
“Within weeks, Presence had flagged several incidents that could have otherwise been missed, including employees forwarding company data to personal accounts during offboarding. The alerts are reliable and actionable, so we've built a full investigation process around them. Although I was skeptical at first, the value was obvious almost immediately.”
“Pistachio has reduced our manual workload to zero with its automated phishing simulations and in‑box delivery of scenario‑based trainings. This has allowed our team to dedicate time to other important security initiatives while Pistachio handles our Security Awareness program seamlessly.”
“Presence automatically detects suspicious behaviour and gives us the visibility we need without constant manual oversight. Within the first few weeks we were already seeing alerts that would have otherwise gone unnoticed as the system learns what is usual and unusual behaviour for our environment.”
“Before Pistachio, security awareness was something we could only offer to a few customers. Today it’s part of every managed service we deliver, and we haven’t had to grow the team to make that happen.”
Fill out the form to book a demo:
Trusted by 1200+ customers & MSPs















